When a business owner asks me "how do we protect ourselves from hackers," there's usually something in their mind already. A sophisticated attacker trying to break through our firewall. Malware sneaking into our systems. Some technical person on the internet doing whatever it is technical people do to steal data.
That's not what actually happens. Not in Nigeria. Not with the businesses I work with.
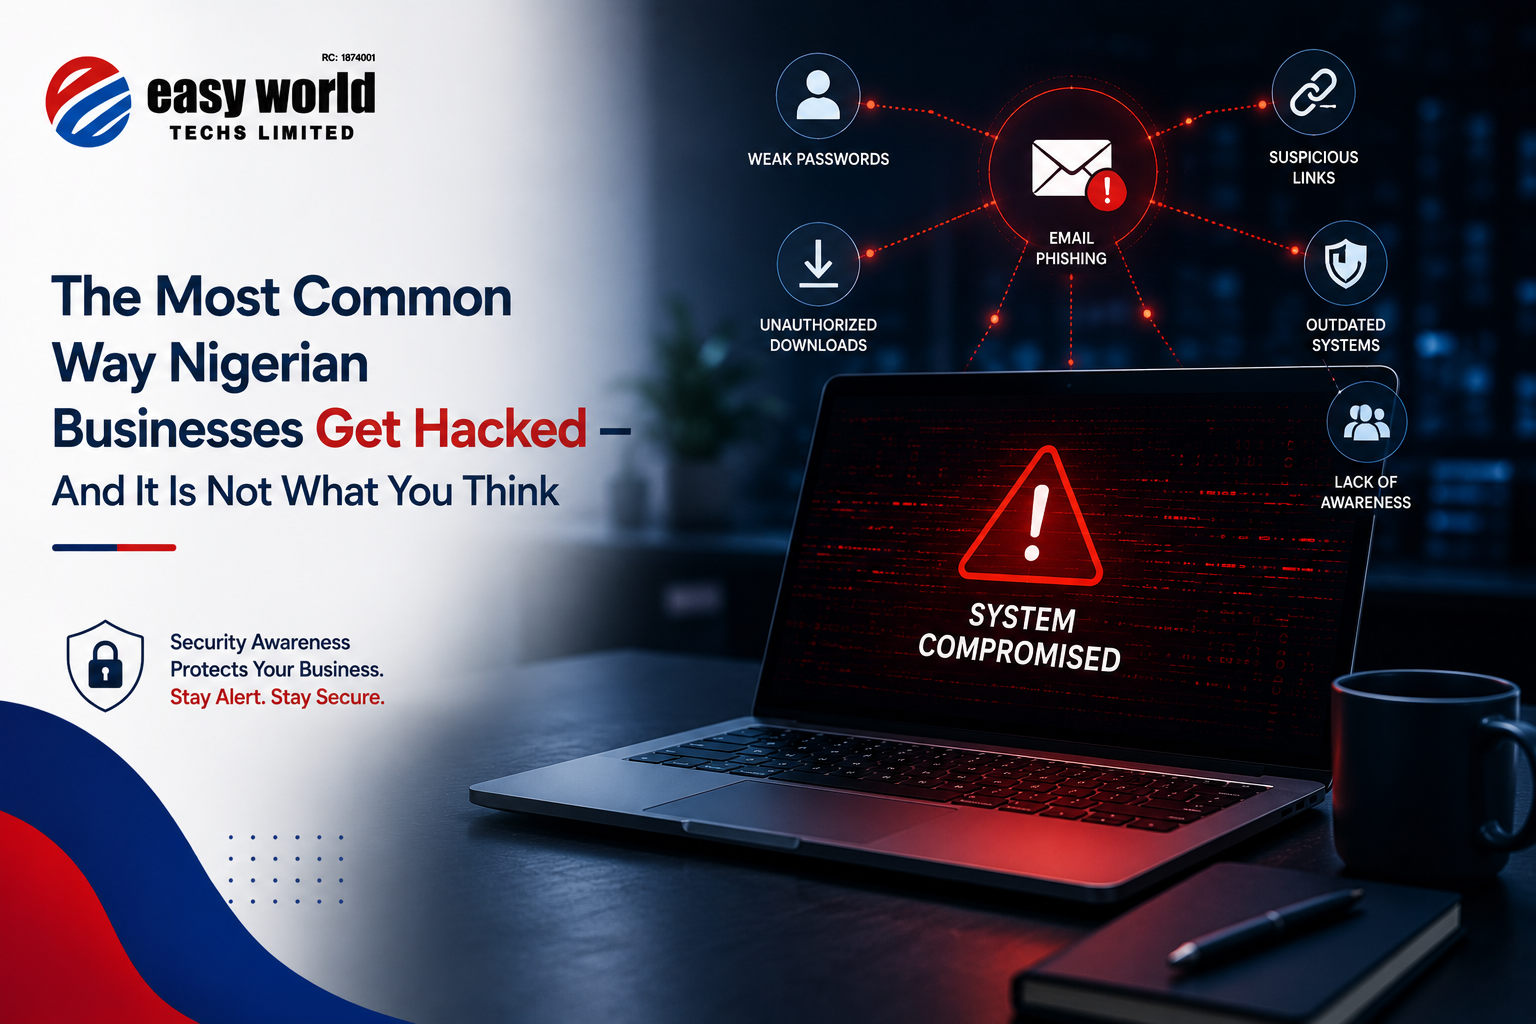
The most common way Nigerian businesses get hacked is someone clicks a link they shouldn't have. That's it. It's boring. It's not dramatic. It doesn't feel like being "hacked" in the way people imagine it.
But it happens to almost every business eventually. And when it does, it's devastating.
Here's What Actually Happens
About eight months ago, I got a call from a client. A financial services firm with about 15 employees. Their accountant had opened an email that looked like it was from their bank. It had the bank's logo. It was formatted correctly. It asked her to click a link and "verify her account details" because of "unusual activity."
She clicked. She entered her username and password on a form that looked exactly like her bank's login page.
Within minutes, someone had accessed the business account and transferred 850,000 naira out.
The accountant felt terrible. The business owner was furious. They both thought: "We got hacked. We need better security software."
But that's not what happened.
What happened was a social engineering attack. An attacker impersonated the bank, made it feel urgent and familiar, and got someone to voluntarily hand over credentials. No sophisticated hacking. No zero-day exploits. Just manipulation.
And here's the thing: a better firewall wouldn't have stopped this. More expensive antivirus wouldn't have stopped it. The password was strong. The account had two-factor authentication.
None of it mattered because the human didn't use the security measure that would have actually helped: skepticism.
Why This Happens So Easily in Nigeria
I notice something specific about how attackers target Nigerian businesses. They don't try to break in through technical vulnerabilities. They go after the humans.
And there are three reasons they do this:
First, it works. You can spend thousands of naira on a sophisticated attack that might fail, or you can send a phishing email to 100 people and get one person to click. The math is easy.
Second, Nigerians are trusting people. I mean this genuinely, not as an insult. In a high-trust, relationship-based culture, the instinct is to assume good faith. You get an email that looks like it's from someone in authority, from a place you recognize, asking you to do something that seems reasonable, and the automatic response is to help. That's culturally normal.
But attackers know this. They know that a carefully crafted email pretending to be from your bank, or from your boss, or from a government agency, is more likely to work on someone in Lagos or Port Harcourt than on someone in some other context where skepticism is the default.
Third, most businesses have no training on this. Not "no security," but literally no training on how to spot these attacks. An employee has never been told: "If something feels urgent or asks you to verify information, pause. Call the person directly. Don't use the number in the email. Use the number you already know for them."
So when the email comes in, there's no alarm. No pause. Just: "OK, I'll do that."
What These Attacks Actually Look Like
Let me be specific because this matters. These aren't hypothetical. This is what lands in inboxes of Nigerian businesses right now:
The bank impersonation — Email looks like it's from a bank, says there's unusual activity, asks you to click a link and log in. The link goes to a fake page that looks identical to the real one. You enter your credentials. The attacker now has them.
The boss impersonation — An email that looks like it's from your managing director or company owner, asking you to urgently transfer funds or send sensitive documents. It feels urgent. It comes during a busy time when you're not thinking clearly. A lot of times, it's not even a technical attack—it's someone who got an employee list and company structure off LinkedIn and is just gambling that one person will act before asking questions.
The vendor impersonation — You do business with someone. An email comes in that looks like it's from them, asking you to change payment details or update banking information. You've done business with them before, so it feels legitimate. You make the change. Now invoices go to the attacker instead.
The credential harvesting — A link in an email or text message takes you to a page that looks like it's asking you to log into something you use (email, banking app, payment platform). You log in. The page says there was an error. You shrug and move on. The attacker just captured your password.
The document trojan — Someone sends you what looks like a legitimate document or invoice (often through WhatsApp or email). You download it. It has malware embedded in it. Once opened, it installs something on your computer that lets an attacker in.
None of these are sophisticated. None of them require deep technical knowledge from the attacker. They just require a human to make a decision in the moment without thinking about it.
Why Your Current Security Isn't Actually Protecting You
Here's the frustrating part: most businesses have some level of security. Firewalls, antivirus, password requirements, maybe even two-factor authentication.
And almost none of it stops these attacks.
Why? Because the attack vector isn't the system. It's the person.
Two-factor authentication doesn't help if you voluntarily hand someone your password. A strong firewall doesn't help if someone inside your network is the one who clicked the malicious link. Antivirus doesn't catch the attack if the person themselves is the entry point.
This is why I tell businesses: the most expensive security upgrade you can make is training your people.
I'm not talking about a one-hour workshop where someone tells everyone "don't click suspicious links" and everyone nods and forgets about it. I'm talking about real, ongoing training. Regular simulated phishing attacks. Conversations about what to do when something feels off. A culture where people can ask "is this legitimate?" without feeling stupid.
Most businesses in Nigeria aren't doing this. I see it across different industries. They're spending money on technical security, but they've left the biggest door open: their people.
What You Should Actually Do
First, accept that this will happen eventually. Someone in your organization will get an email that looks legitimate and will be one second away from clicking. Accept that, and build your response around it.
Second, set up a training program. Not a scary one. Just: "Here are the patterns to watch for. Here's what we do if you think something might be phishing. Here's the process for requesting changes to account information or payment details."
Third, set boundaries on who can authorize critical actions. If you transfer money, it shouldn't be one person clicking a link. It should be a conversation. A verification call using a known number. A process that requires a second person to confirm.
Fourth, have a response plan for when it happens. Not if. When. Who do you call? What do you do in the first hour? How do you isolate the compromised account? How do you communicate with your bank or payment processor? Most businesses figure this out while they're panicking, which is too late.
Fifth, teach people to slow down. This is the underrated one. Most successful phishing attacks rely on urgency. "Verify your account immediately." "Transfer funds urgently." "Update this information now." If your culture is one where people slow down and verify before acting on urgent requests, you cut your risk dramatically.
I'd estimate that 80% of the breach situations I've seen would have been prevented if one person had just called the sender to verify before acting.
The Real Cost of Getting This Wrong
The 850,000 naira that got stolen from that financial services firm? That was recoverable eventually, after a lot of work, a lot of stress, and a lot of money spent with lawyers and their bank trying to trace it.
But there were other costs that don't show up in the incident report.
The accountant was embarrassed. She's still defensive about security. The trust in the team shifted—people started questioning each other's actions. The owner spent weeks on this instead of growing the business. They hired a security consultant who sold them expensive software that didn't actually solve the problem.
And the attacker? If they were caught, it would be hard to prove. They're probably in a different country. They've moved on to the next business.
This is why it matters. Not because you're going to get hacked by a sophisticated attacker with dark web skills. But because you're going to get targeted by someone who knows that most businesses are trusting, that most employees will help if you ask nicely, and that most security is built to stop technical attacks, not human ones.
Have you seen something in your business that felt like it could have been an attack? Or do you have a process your team uses that actually catches this stuff? I'm curious what actually works because it's rarely what the security companies are selling.